Audit logs
The Audit logs tab (Settings, platform administrators only) traces mutating actions performed by users — create, update, delete — on resources managed by the Control Panel: applications, accounts, permissions, volumes, namespaces, Git secrets, identity providers…
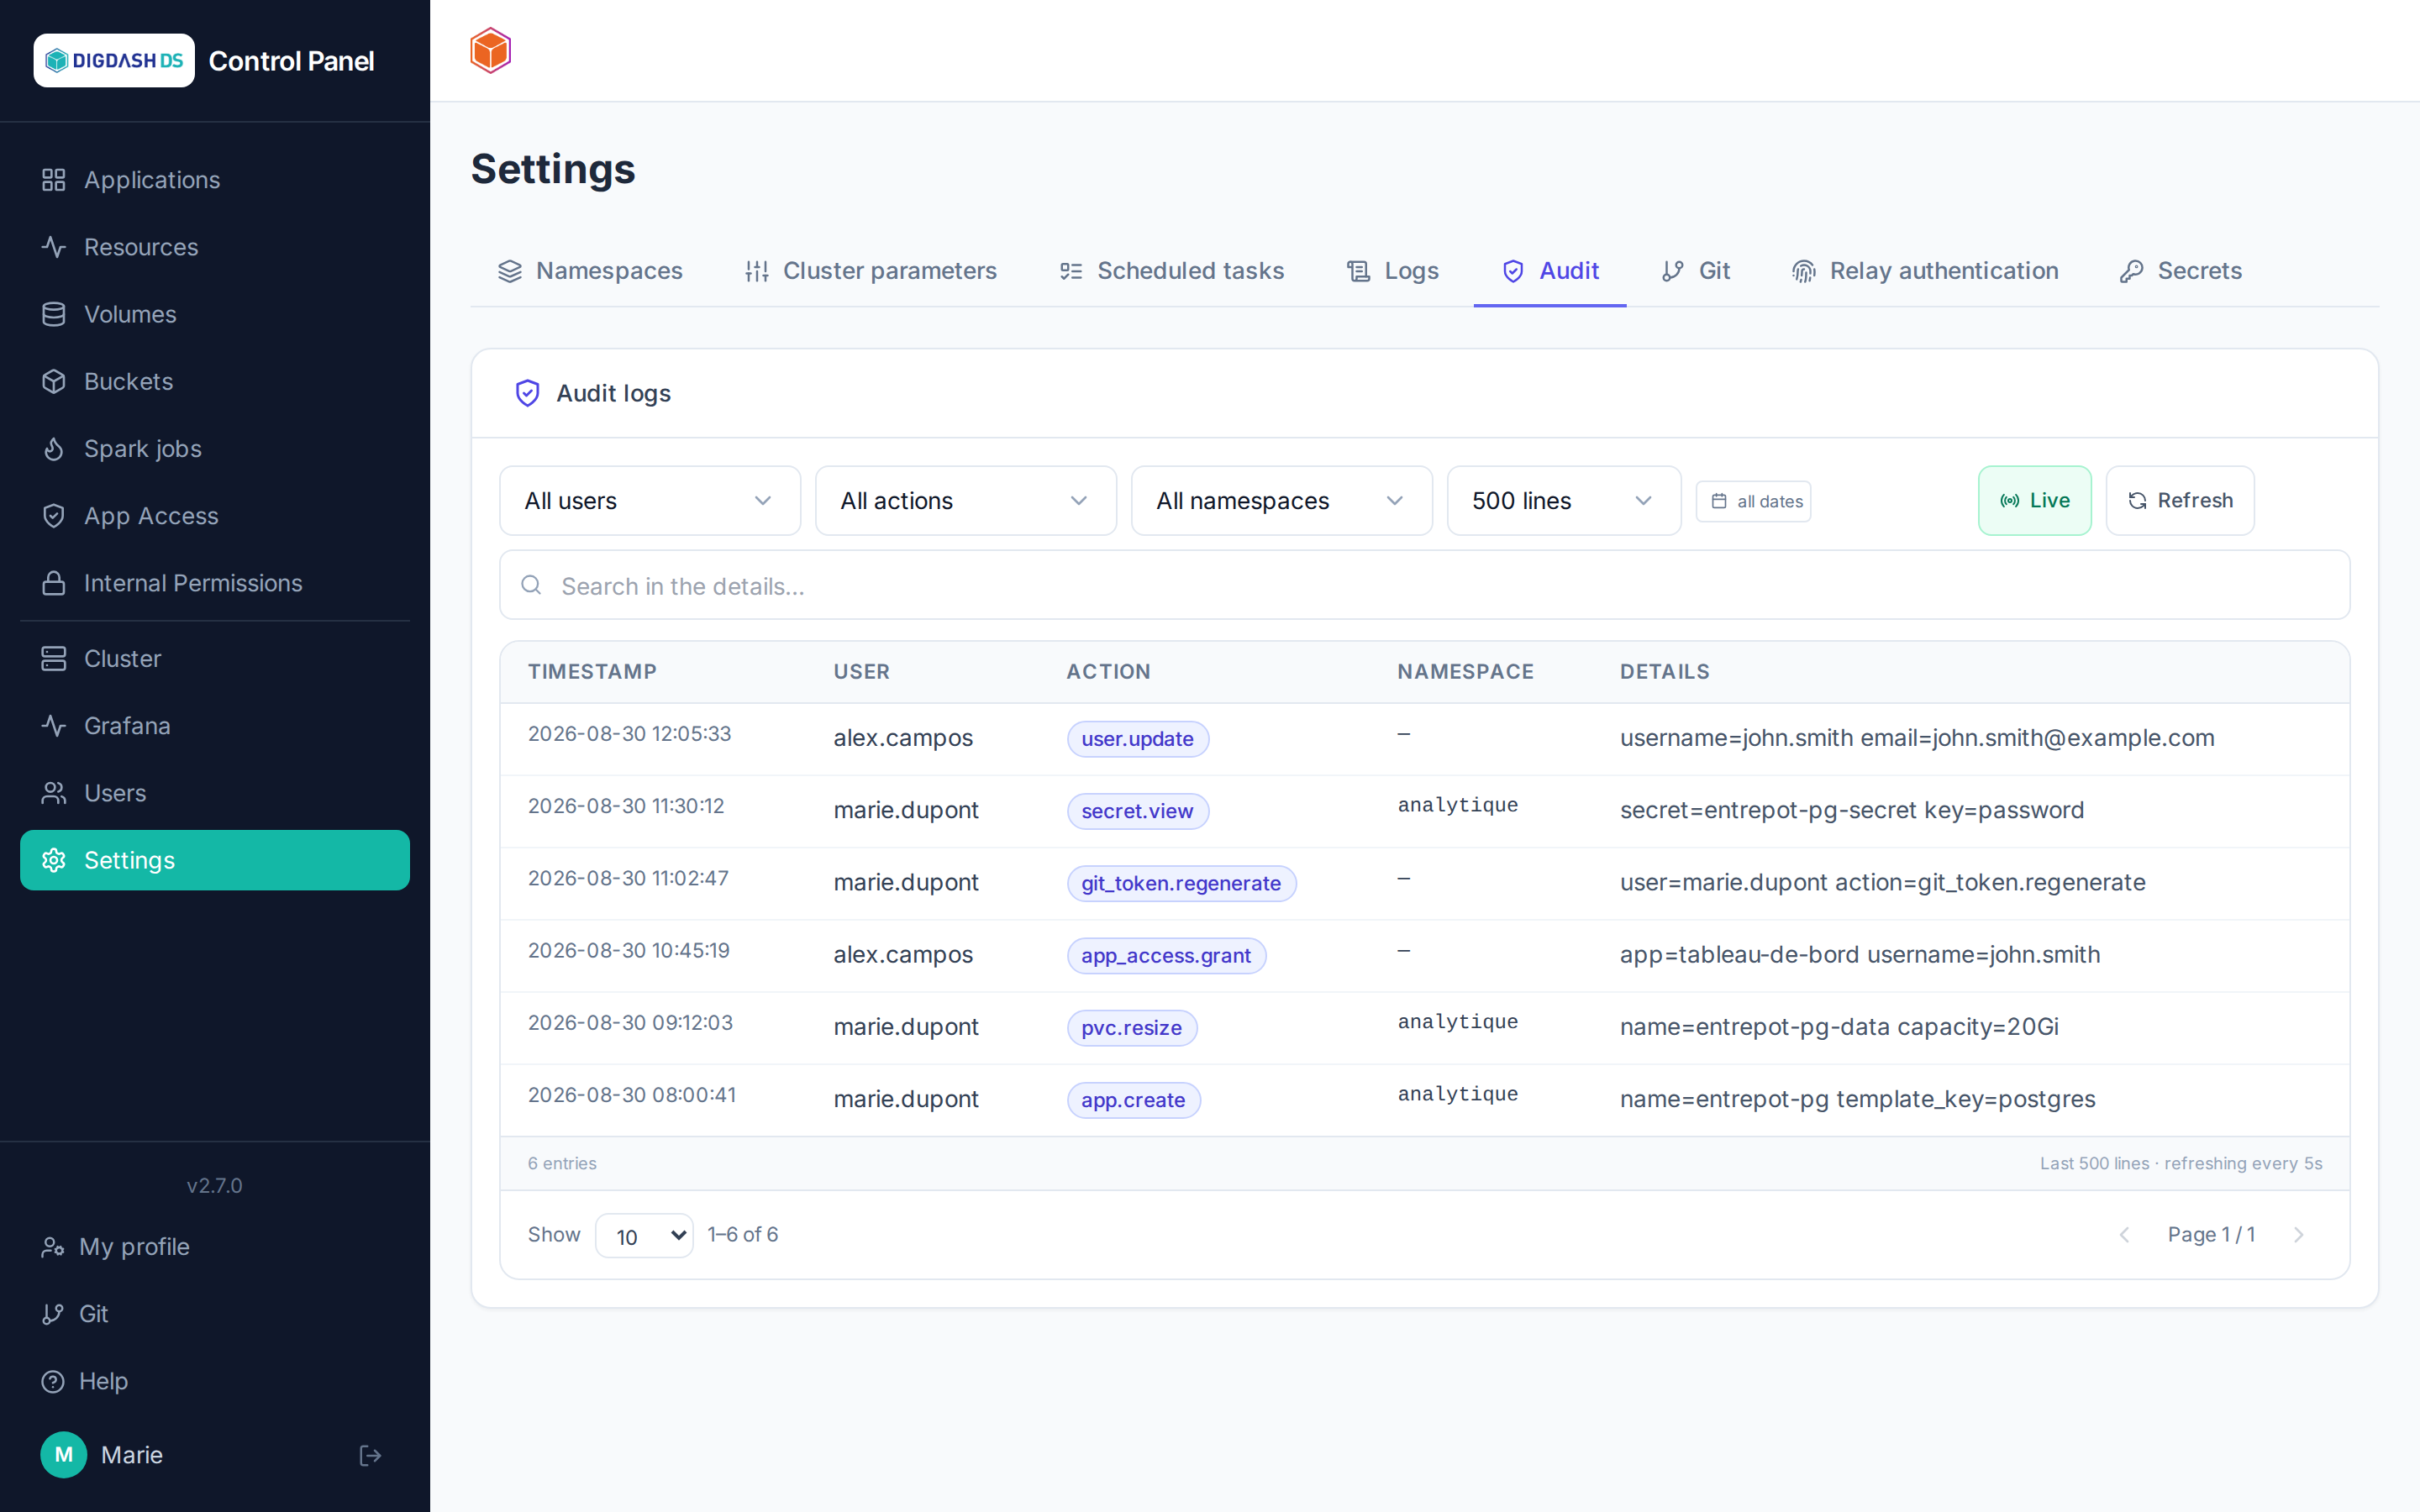
What isn't traced here
Only successful actions are logged — an attempt rejected by a permission check or a technical error doesn't appear in this log (it stays visible in the general technical logs). Plain data reads generally aren't traced, except reads considered sensitive: viewing a personal Git token (git_token.view) and viewing or copying a Kubernetes secret's value (secret.view, secret.copy — see Secrets).
Table columns
| Column | Content |
|---|---|
| Timestamp | Date and time of the action, in the browser's time zone. |
| User | The username who performed the action — anonymous for an unauthenticated action (normally never happens, since these actions require a session). |
| Action | A short, stable identifier in resource.verb form, e.g. app.create, user.delete, pvc.resize, git_token.regenerate — see examples below. |
| Namespace | The relevant namespace, when the action depends on one (an application, a PVC…) — empty for cross-cutting actions (user management, identity providers…). |
| Details | Identifiers specific to the action's target (application name, pod, volume, group…), as key=value pairs, specific to each action type. |
Action examples
| Action | Domain |
|---|---|
app.create, release.delete, release.scale, deployment.restart, workload.update |
Application lifecycle |
pvc.create, pvc.resize, pvc.delete, pvc.clone, pvc.snapshot, snapshot.restore, snapshot.delete |
Volumes and snapshots |
app_access.grant, app_access.revoke, app_access.set_profiles, application_permission.delete |
Application access |
user.create, user.update, user.delete, user.bulk_update, user.bulk_delete |
User accounts |
group.member_add, group.member_remove, group.namespace_permission_add, group.namespace_permission_remove, group.delete |
Groups and permissions |
namespace.create, namespace.quota_update, namespace.quota_bulk_update, namespace_permission.delete |
Namespaces and quotas |
git_token.view, git_token.regenerate |
Personal Git access token |
identity_provider.create, identity_provider.update, identity_provider.delete, identity_provider.mapper.create, identity_provider.mapper.update, identity_provider.mapper.delete |
Identity brokering (see Identity brokering) |
secret.view, secret.copy |
Viewing or copying a Kubernetes secret value (see Secrets) |
No secret values are ever logged
A password, token or secret key never appears in plain text in an action's details — only the fact that it changed is traced (e.g. password_changed=True).
Filtering and following the log
- User, Action, Namespace: dropdowns populated dynamically from values seen so far.
- Search: full-text filter on the Details column.
- Date range: restricts to entries whose timestamp falls within the chosen interval.
- Line count: volume of log lines fetched from the server (100 to 5000).
- Live: auto-refreshes every 5 seconds; Pause freezes the display without stopping collection.